Finding my first web vulnerability
Some time ago, I was playing Valorant, one of my favorite video games. I played poorly and eventually lost while having a really bad KDA (Kills/Deaths/Assists in the realm of 4/24/5). I got really tilted and slammed my hand really hard onto the armrest of my chair. It broke :(.
So, I contacted the support of the manufacturer of my gaming chair. A few emails went by, and I had sent my personal information and told the support what spare part I needed. Some days later, I received an email telling me to go to a website and pay.
After I clicked on the link, I was directed to a website that looked like it was old or not really finished. I took a glance at the URL and was a little confused. The link looked like this:
example.com/shipstream/payment.php?order=200004416&paymentID=24f9c13b2dc5c6e9ed1a96f08b3b62690413a6815a2c149bdc9c79c0bcd98e99
I’m a newbie to the field of IT security, even though I was currently in my practical phase in the SAP BTP Trust Team, but I was wondering how they handled authentication since I hadn’t logged in to a user account or anything similar. On the website, there was only a price, order ID, the article that I was trying to order, and a link to PayPal. It turns out they didn’t really handle it. It seems like they relied on the fact that no personal data was displayed. I started slowly by trying to manipulate the order field in the URL. I decreased the value by one, et voila I now saw a different order. The payment ID remained the same, but the price that one should pay changed from order to order.
Later, I found out that this sort of attack is called an Insecure Direct Object Reference (IDOR). It’s a vulnerability where the application exposes internal implementation objects like files, directories, database records, or keys, without proper authentication checks. This allows attackers to manipulate references to access unauthorized data.
Now, I was thrilled because I had just discovered my first web vulnerability. Feeling a bit lightheaded and unaware of potential consequences, I continued experimenting on my device without anonymity precautions. I attempted basic SQL injections like true;--, but aside from specific error logs, I found nothing new.
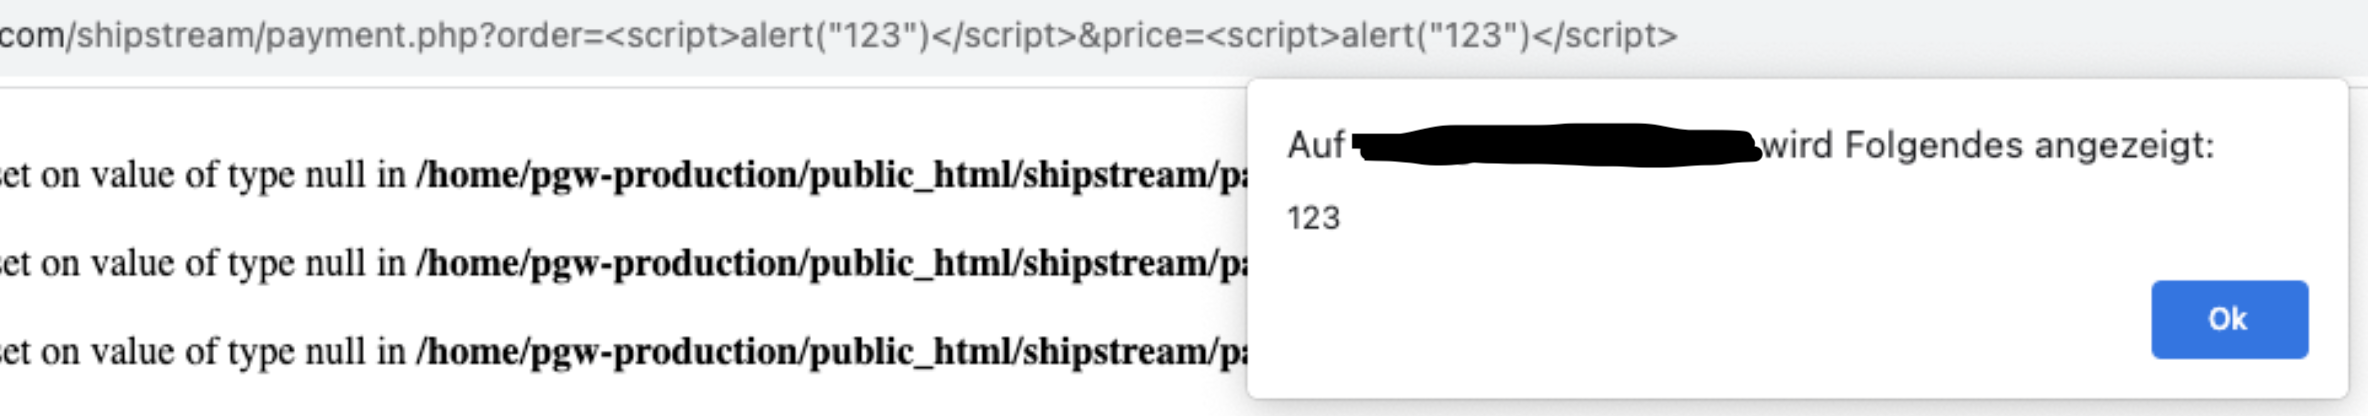
After sharing my experience with colleagues from the team I was working on, who were developers and security experts, we recreated my findings in a meeting. They advised documenting the vulnerabilities with screenshots and notifying the website owner. We decided to try cross-site scripting, which worked like a charm:
(We also received some source code snippets for further analysis, possibly in another blog post.)
I documented the changes and sent an email to the support address from the website. It went something like, ‘Hi, I’m an IT student, and I found something on your website.’ A day later, I received a thankful response, promising to address the issue. A few hours later, to my surprise, they informed me they would send my 40 euro spare part for free. It’s moments like these that remind me of the positive impact one can have by taking the initiative to reach out and make a difference.